Popular Searches

Digital Marketing AI Data Science Machine Learning Data Analytics SEO Social Media Marketing Python JavaScript

Expert

12 Months Course

Advanced

6 Months Course

Beginner

3-4 Months Course

Short Course

1 Month Course

Free

Free Courses

AI-Integrated Offensive Security Training

Expert Bug Bounty Course with AI-Powered Hacking Labs

4.9/5 from 1,043 reviews 25,000+ learners trained 250+ hiring partners

DizitalAdda's Expert Training in Bug Bounty is a 4-month, 96-hour bug bounty course that takes you from recon to a triage-ready report. You practise OWASP Top 10, API and JWT attacks, SSRF and AI-assisted hunting on authorised targets, with mentor feedback, a certificate and 100% Placement Assistance.

  • 4 Months / 96 Hours, Hybrid (Online + Offline)
  • AI-Integrated Training in Every Module
  • Bug Bounty with Gen AI: AI Recon and LLM Security Testing
  • Recon-to-Report Pipeline on Authorised Live Scopes
  • OWASP Top 10, API, SSRF, JWT and Request Smuggling
  • Certificate and 100% Placement Assistance
Live recon workflows AI-powered hacking labs Bug reporting practice
Free Career Counselling

Talk to a Cyber Mentor

Get a free call to choose the right path for bug bounty, VAPT or ethical hacking.

🔒 Your details are private. A mentor calls you within 24 hours.

  • Free demo class
  • Online & offline batches
  • 100% Placement Assistance
Duration: 4 Months / 96 Hours Mode: Hybrid (Online + Offline) Placement: 100% Placement Assistance Rating: 4.9 / 5 Level: Expert

Key Skills Covered in This Bug Bounty Course

Reconnaissance Subdomain Enumeration OWASP Top 10 API Security SSRF IDOR JWT Attacks Request Smuggling Burp Suite Nuclei Recon Automation AI-Assisted Recon Prompt Injection Testing CVSS Scoring Bug Report Writing Responsible Disclosure

Why Choose DizitalAdda's Expert Bug Bounty Course

Your Benefits
01Live web exploitation labs
02AI-integrated training in every module
03Bug bounty with Gen AI module
04Recon automation workflows
05Bug report writing practice
06Mentor feedback on submissions
07100% Placement Assistance
08Offline and online training modes

Key Highlights

  • Hands-on recon to report workflow
  • Practice across OWASP Top 10 scenarios
  • API, token and AI app security testing
  • Live doubt solving with expert mentors
  • Career guidance for pentest and bounty paths
  • Practical labs for web and API security
  • Flexible weekday and weekend batches
  • Interview and reporting preparation
Talk to an Expert

CYBER SECURITY CAREER SUPPORT

★★★★★ Practical learning backed by 100% Placement Assistance

Build Offensive Security Skills That Hiring Teams Value

This bug bounty course with placement support is built for learners who want hands-on proof, not just theory. You train on realistic recon and validation workflows, use AI to work faster, sharpen reporting quality, and prepare for bug bounty, VAPT, and cyber security analyst roles.

92% Learners moved into security tracks
7.8L Highest reported CTC
250+ Hiring and referral partners
25000+ Tech learners trained

Course Roadmap

What Will You Learn?

Nine practical modules take you from recon to live target practice. Every module of our bug bounty course is AI-integrated, and a dedicated Gen AI module teaches you to test AI apps and chatbots.

Foundations & Reconnaissance

  • How bug bounty programmes, scope and rules work
  • HackerOne, Bugcrowd and Intigriti walkthrough
  • Passive recon: OSINT, Shodan and certificate logs
  • Subdomain enumeration with Amass and Subfinder
  • Live host probing and asset mapping with httpx
  • Content discovery and fuzzing with ffuf
Amass Subfinder httpx ffuf

AI-Integrated Bug Bounty Workflow

  • Using AI assistants to plan recon and sort results
  • AI-assisted JavaScript and endpoint analysis
  • Writing recon scripts faster with AI
  • Checking every AI finding by hand to avoid false reports
  • AI usage rules on bug bounty programmes
ChatGPT Claude Gemini AI Recon

Core Web Vulnerabilities (OWASP Top 10)

  • SQL injection and command injection
  • Reflected, stored and DOM XSS
  • Broken authentication and session flaws
  • Access control bugs and IDOR
  • CSRF and insecure file upload
OWASP Top 10 Burp Suite XSS IDOR

Advanced Vulnerabilities & Exploitation

  • SSRF and cloud metadata exposure
  • Open redirect and clickjacking
  • Web cache poisoning and HTTP request smuggling
  • JWT attacks and CORS misconfiguration
  • Chaining small bugs into high-impact reports
SSRF JWT CORS Bug Chaining

API Security Testing

  • Mapping REST and GraphQL APIs with Postman and Burp
  • Broken object and function level authorisation
  • Mass assignment and parameter tampering
  • Rate limit and auth flow weaknesses
  • OWASP API Security Top 10
Postman GraphQL BOLA API Top 10

Bug Bounty with Gen AI: LLM & AI App Security

  • OWASP Top 10 for LLM applications
  • Direct and indirect prompt injection
  • Data leakage and insecure output handling
  • Testing in-scope AI chatbots and plugins
  • Writing clear reports for AI vulnerabilities
Gen AI Prompt Injection LLM Security

Real-world Practice & Automation

  • Building your own practice lab with Kali Linux
  • Burp Suite extensions for faster testing
  • Bash and Python recon automation
  • Writing and running Nuclei templates
  • Monitoring targets for new assets
Kali Linux Python Bash Nuclei

Reporting, Duplicates & Triage

  • Report structure that triage teams accept
  • CVSS v3.1 severity scoring
  • Tactics to reduce duplicate reports
  • Talking to triagers and handling disputes
  • Responsible disclosure and legal ethics
CVSS Report Writing Disclosure

Final Projects & Live Target Practice

  • Hunting on authorised live programmes with mentors
  • Mock triage and peer review
  • Portfolio of write-ups and lab reports
  • Interview preparation and career plan
Live Scope Portfolio Career

Not sure if you are ready? Book a free demo of our bug bounty course →

Career Skills Stack

What Makes You Job-Ready in Bug Bounty and Web Security

Beyond tools, the course builds the thinking, methodology, AI-assisted workflow and communication needed to validate issues and present them professionally.

Advanced reconnaissance
Subdomain and asset discovery
Attack surface mapping
Content discovery and fuzzing
Manual validation techniques
AI-assisted recon and analysis
OWASP Top 10 testing
Authentication and session flaws
SSRF and access control analysis
API testing workflows
LLM and prompt injection testing
Proof-of-concept building
Bug bounty reporting
Duplicate reduction strategy
Severity and impact writing
Responsible disclosure ethics
Interview and CV readiness
Freelance and platform guidance

Hands-On Labs

Practice on Realistic Security Workflows

Each project block is built to move you from finding signals to validating impact, documenting proof, and presenting a clean security report.

12 Hours + guided assignments

Recon Sprint on Live Scope

Build a repeatable recon pipeline using passive and active asset discovery, content discovery, and prioritisation for real bug bounty targets.

  • Subdomain discovery with validation
  • Asset tagging and prioritisation
  • httpx, ffuf, and nuclei workflow design
  • Recon notes and scope hygiene
15 Hours

Burp Suite Exploitation Lab

Work through hands-on labs for authentication, business logic, access control, IDOR, CSRF, XSS, and request manipulation.

  • Proxy, repeater, intruder, and extender usage
  • Session and token handling
  • Manual testing for logic flaws
  • Evidence capture and reproducibility
10 Hours + test cases

API Security Assessment

Assess REST and JSON APIs for broken object level authorisation, rate limit issues, weak auth flows, and parameter tampering.

  • API collection mapping
  • Auth flow tampering
  • Access control and object ID checks
  • Structured findings sheet
8 Hours

AI Chatbot Security Lab

Test a practice AI chatbot for prompt injection, data leakage and unsafe output, then write the finding the way bounty programmes expect.

  • Direct and indirect prompt injection
  • System prompt and data leakage checks
  • Unsafe output and plugin abuse
  • AI vulnerability report format
8 Hours

SSRF and Cloud Misconfiguration Practice

Learn safe SSRF validation patterns, metadata exposure paths, and cloud misconfiguration indicators in a controlled training setup.

  • URL parser edge cases
  • Metadata path testing
  • Filter bypass reasoning
  • Impact articulation
6 Hours

Bug Report Writing Workshop

Turn valid findings into high-quality reports with clear impact, reproduction steps, remediation guidance, and supporting evidence.

  • Title and severity framing
  • Step-by-step reproduction format
  • Screenshots, HAR, and request proof
  • Triage-friendly communication

Security Tools

Hands-on Bug Bounty Training with Industry Testing Tools

Our bug bounty training uses the core tools for reconnaissance, endpoint discovery, request manipulation, API testing and reporting, plus AI assistants that speed up recon and analysis.

What Our Learners Say

"The biggest difference was learning how to validate findings properly. The reporting part alone made me think like a real security tester."

- Shivam Arora, Security Research Intern

"I had seen tools before, but this course finally connected recon, manual testing, and impact. That changed how I hunt on real programs."

- Kashish Mehta, Bug Bounty Learner

"The labs and mentor reviews helped me move from random scans to structured testing. That also improved my interview confidence."

- Danish Khan, Junior VAPT Analyst

Our Cyber Security Programs

Choose a practical learning path based on your current level, specialization goals, and time commitment.

Expert Training in Cyber Security and Ethical Hacking
Expert 12 Months
★4.9(1,120 ratings)
Job Oriented Course

Expert Training in Cyber Security and Ethical Hacking

A complete offensive and defensive security program covering networking, VAPT, Linux, malware basics, and career readiness.

Explore Program →
Advanced Certification in Cyber Security and Ethical Hacking
Advanced 6 Months
★4.8(860 ratings)
Job Oriented Course

Advanced Certification in Cyber Security and Ethical Hacking

A practical program for learners who want deeper exploitation, tools training, and structured cyber lab exposure.

Explore Program →
Certification in Digital Forensic and Cyber Investigation
Specialized 4 Months
★4.8(640 ratings)
Job Oriented Course

Certification in Digital Forensic and Cyber Investigation

Focused training for evidence handling, investigation flow, forensic tooling, and cyber incident understanding.

Explore Program →

Choose Your Perfect Learning Path

Compare our courses and find the right fit for your cyber security journey

Expert Level

Expert Training in Bug Bounty

4 Months

  • Recon to report pipeline
  • OWASP and API testing focus
  • Live target methodology
  • AI-integrated and Gen AI security labs
  • Bug report writing
  • Mentor-led validation
  • 100% Placement Assistance

Perfect For:

Learners targeting bounty hunting, web pentesting, and offensive security work

Advanced Level

Advanced Cyber Security & Ethical Hacking

6 Months

  • Networking and Linux foundation
  • Ethical hacking tool usage
  • VAPT lab practice
  • Python basics for security
  • Guided hands-on assignments
  • Structured mentor support

Perfect For:

Learners who want a wider cyber security base before specializing

Foundation Level

Foundation in Cyber Security and Ethical Hacking

4 Months

  • Cyber security basics
  • Networking essentials
  • Introductory web security
  • Lab orientation
  • Career awareness
  • Beginner-friendly pace

Perfect For:

Freshers and non-technical learners starting from zero

Specialised Level

Digital Forensic and Cyber Investigation

4 Months

  • Evidence handling and chain of custody
  • Disk and memory forensics
  • Incident investigation flow
  • Forensic tooling labs
  • Case reporting
  • Career support for forensic roles

Perfect For:

Learners who want to investigate cyber incidents and work with digital evidence

Your Path to Success

Your Journey With Us

From day one to your first valid bug report — here's exactly how we take you there, step by step.

Step 1
Step 01

Enrollment

Meet your course counsellor, choose the right batch, and start with a clear learning roadmap for bug bounty hunting.

Course Selection1-on-1 CounsellingFlexible Batches
Step 2
Step 02

Training

Attend live expert-led classes on recon, OWASP Top 10, API testing, web exploitation and AI security — with hands-on labs every week.

Live Expert Classes9 Modules, 96 HoursReal Lab Access
Step 3
Step 03

Live Projects

Run recon sprints and exploitation labs on authorized scopes — and build a verified portfolio of write-ups and reports.

Real Scope PracticeVerified PortfolioMentor Reviews
Step 4
Step 04

Certification

Earn DizitalAdda's Bug Bounty certification with Skill India recognition — backed by a portfolio of real lab submissions.

DizitalAdda CertifiedSkill IndiaLab Portfolio
Step 5
Step 05

Bug Bounty Practice

Start responsibly hunting on HackerOne and Bugcrowd with mentor support — validating, reporting, and building your bounty history.

HackerOne / BugcrowdGuided SubmissionsMentor Support
Step 6
Step 06

Career / Freelancing

Get placed as a pentester, VAPT analyst, or SOC professional — or freelance with your bug bounty portfolio as your credential.

100% Placement Assistance250+ PartnersFreelance Guidance
For Everyone

Who Should Join This Expert Bug Bounty
Training Course
?

This bug bounty hunting course is built for people who are serious about web security. Here is exactly who will benefit most.

IT Professionals

Transition into offensive security or add bug bounty as a high-income skill — with flexible batches, expert mentorship, and a structured recon-to-report pathway that fits around your current job.

Students & Graduates

Graduate with a portfolio of real recon reports and lab write-ups that prove hands-on skill — so you stand out over every applicant who only has theory and no field exposure.

Developers

Understand how attackers think — learn to find IDOR, XSS, SSRF, and broken auth in APIs and web apps so you can build more secure products and command higher rates as a security-aware dev.

Ethical Hackers

Specialise in web and API security — moving beyond basic CEH theory into real vulnerability chains, bounty platform workflows, and responsible disclosure that generates actual results.

Career Switchers

Switch into cyber security from any background — with a 4-month structured roadmap, a verified portfolio, and a career team that helps you frame your transition to security recruiters.

Freelancers

Turn your curiosity into paid work — by learning structured recon, exploitation, and reporting skills that let you take VAPT freelance contracts or earn bounties on live programs.

What Our Cyber Security Students Say

Student Reviews

"I recently joined the Foundation in Cyber Security & Ethical Hacking course at DizitalAdda, Delhi. The training is easy to understand, even for beginners. I learned about networking, security fundamentals, and ethical hacking concepts. The practical sessions make learning more interesting."

AS
Aarav SharmaFoundation Cyber Security Student

"The Advanced Certification in Cyber Security at DizitalAdda helped me understand cybersecurity concepts in much more depth. The trainers explain technical topics with practical examples. I particularly liked the hands-on learning approach."

VS
Vikram SinghAdvanced Cyber Security Student

"I was looking for an institute where I could learn ethical hacking practically. DizitalAdda offers a structured learning experience with practical exercises. The trainers explain different tools and techniques step by step."

PP
Priya PatelEthical Hacking Student

"As a beginner, I was initially confused about where to start with cybersecurity. The Foundation course at DizitalAdda made things easier. The concepts are explained in simple language, and the learning environment is supportive."

RV
Rohan VermaFoundation Cyber Security Student

"I wanted to gain practical knowledge of ethical hacking rather than just study definitions. The training approach at DizitalAdda focuses on understanding tools, techniques, and security concepts through practical exercises."

AK
Amit KumarEthical Hacking Student

"The six-month Advanced Certification programme offers a structured way to learn cybersecurity. I liked how the topics are covered step by step, starting with fundamentals and moving towards advanced concepts."

SB
Siddharth BanerjeeAdvanced Cyber Security Student

"Cybersecurity was a completely new field for me. The trainers at DizitalAdda helped me understand ethical hacking, network security, and different cybersecurity fundamentals. A useful learning experience."

PN
Pooja NairEthical Hacking Student

"I had almost no technical knowledge when I started learning ethical hacking. The Foundation course helped me build my understanding from the basics. I appreciate the trainers for being patient and supportive."

AR
Arjun RaoFoundation Cyber Security Student

"The advanced ethical hacking training helped me explore topics beyond basic cybersecurity. I enjoyed learning about vulnerability assessment, network security, and security testing in a structured manner."

DS
Deepak SaxenaAdvanced Ethical Hacking Student

"I would recommend exploring DizitalAdda if you are interested in learning cybersecurity and ethical hacking. The course structure covers important fundamentals, and the trainers make technical topics easier to understand."

TD
Tanvi DeshmukhCyber Security Student

Bug Bounty Certification

DizitalAdda's Bug Bounty Course
Certification Gets You Hired!

About DizitalAdda's Certification

As a bug bounty certification course, DizitalAdda's Expert Bug Bounty Certification is awarded after completing a 4-month hands-on training programme — and it is recognised in the security industry because it comes with a verified portfolio of recon reports, lab write-ups, and responsible disclosure submissions, not just a multiple-choice exam score.

The certification covers the complete bug bounty workflow: reconnaissance, subdomain enumeration, OWASP Top 10 testing, API security, SSRF, JWT abuse, AI-assisted hunting, LLM security testing, report writing, and bounty platform methodology. Your portfolio includes credentials from DizitalAdda, Skill India, and Digital India — each tied to a specific lab or project you completed.

This is your launchpad to roles paying ₹4.8–7.8 LPA at companies like TCS Cyber, Deloitte, EY, PwC, and 250+ hiring partners — or to earning bounties directly on HackerOne and Bugcrowd. 92% of our learners move into security tracks, backed by 100% Placement Assistance.
Next Batch Starts In:
01: 09: 54
Only 8 seats left

Learn From The Best

Learn From Industry
Expert Trainers

At DizitalAdda, your trainers are full-time industry professionals who work on live projects and deliver results every day.

What We Have Achieved?

  • DizitalAdda has trained 25000+ students and working professionals through practical Digital Marketing, Cyber Security, and Bug Bounty programs designed for real industry needs. With hands-on learning, live labs, and career-focused training, the institute has helped learners build successful careers in top companies, startups, and security firms across India.
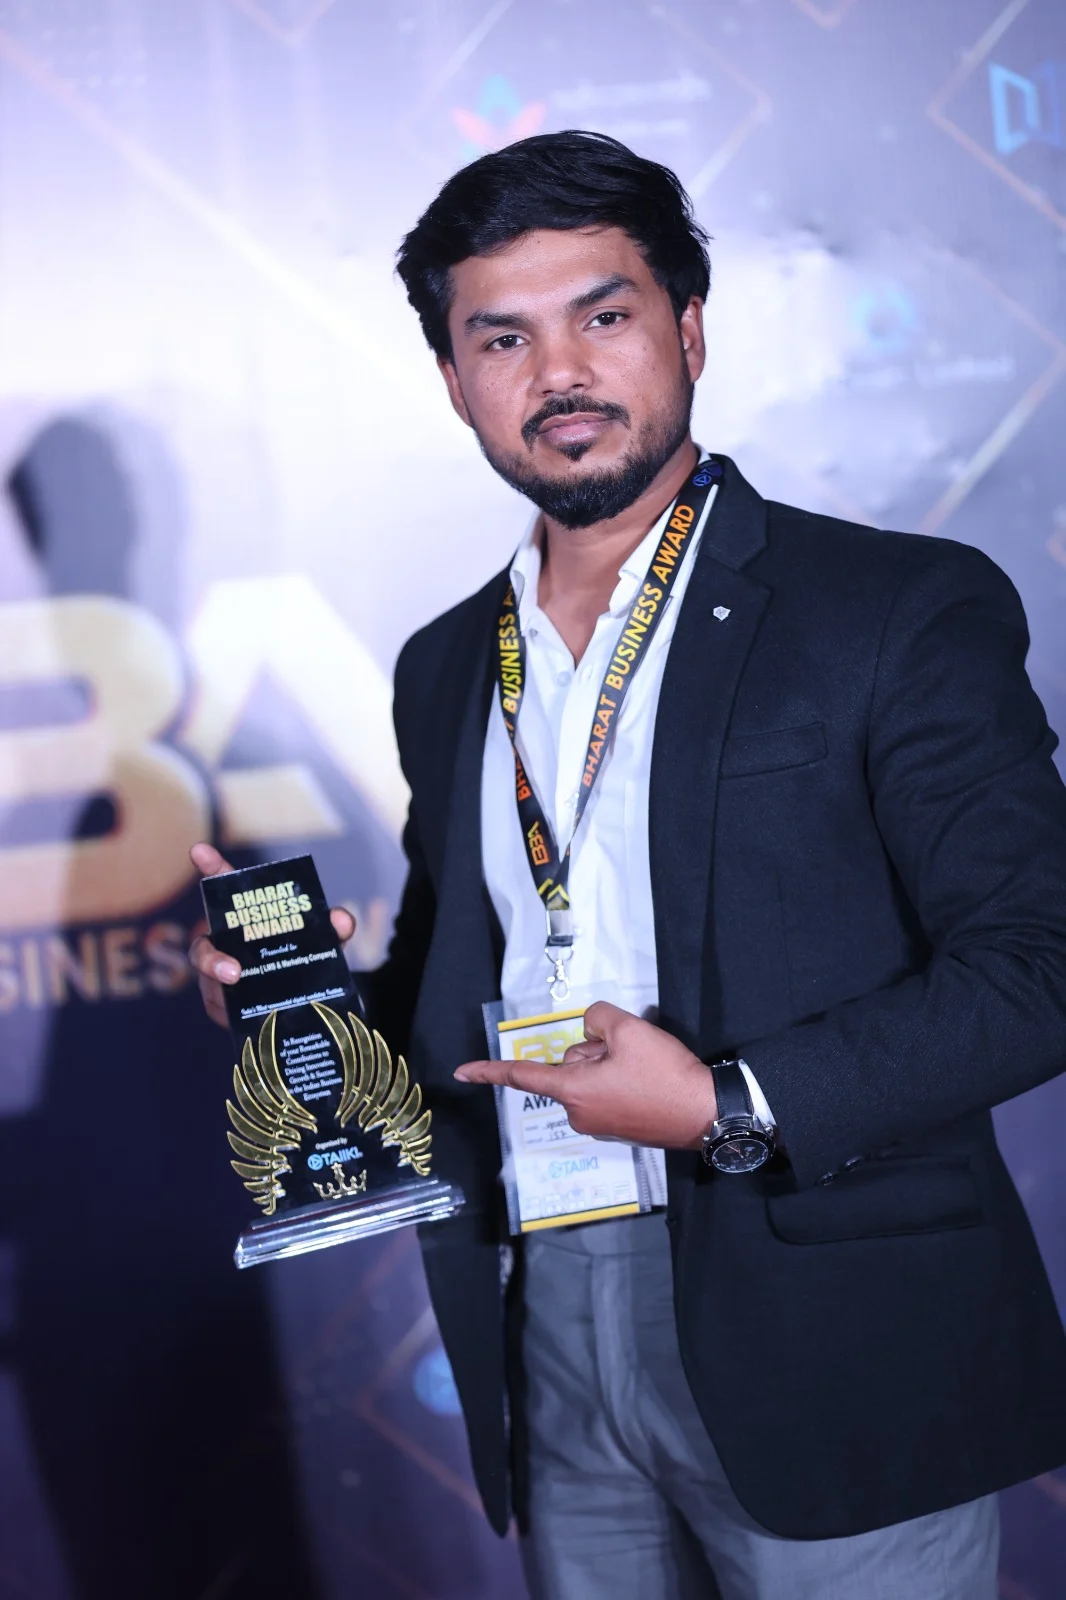
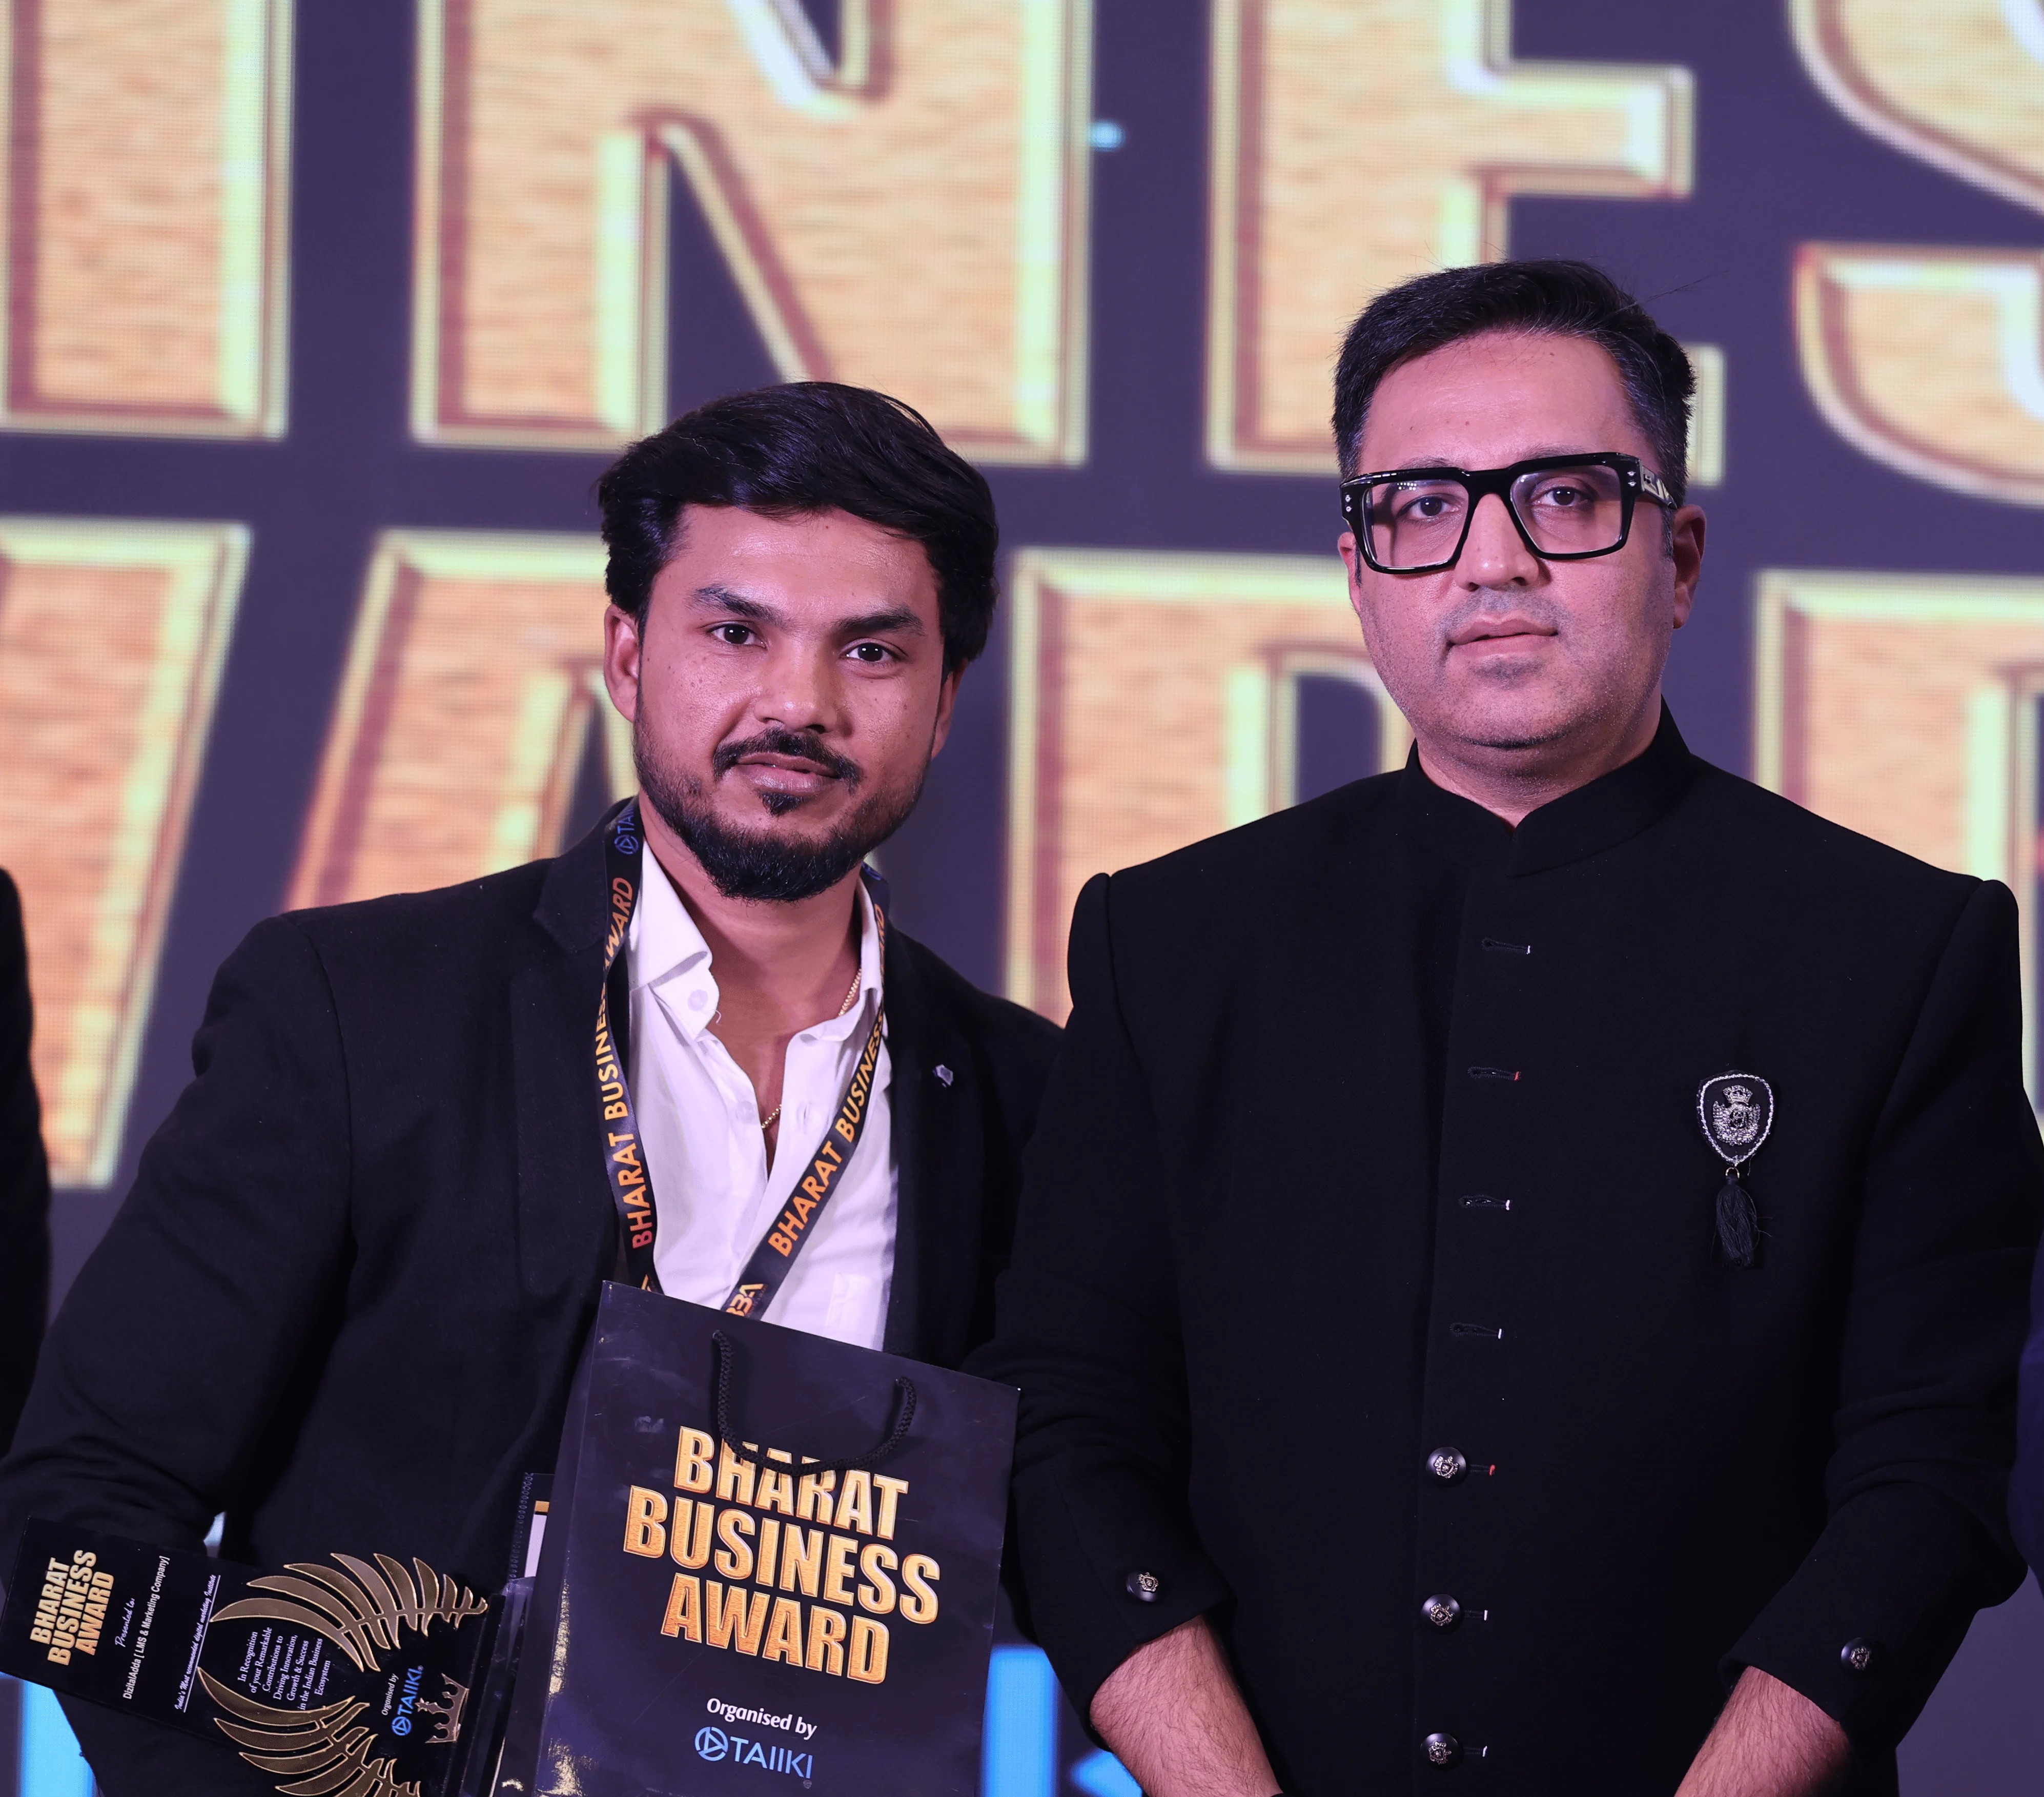
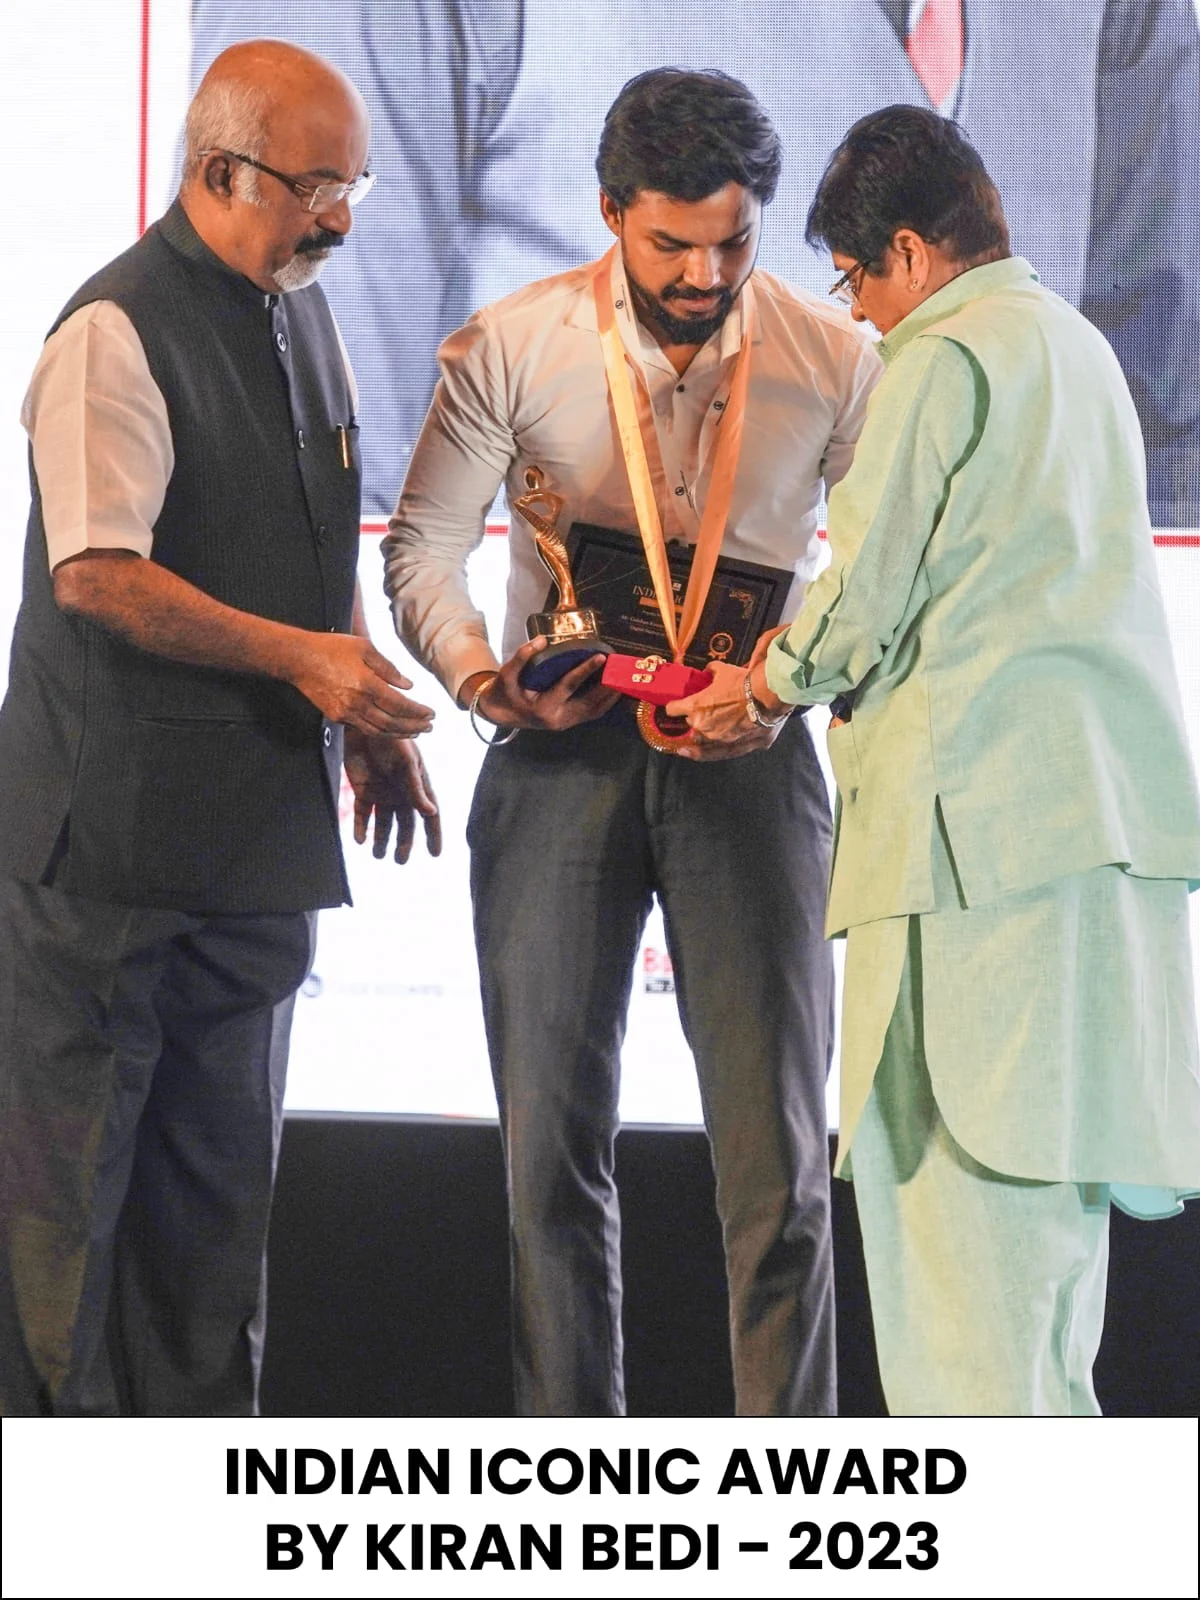
  • The institute's contribution to skill-based education has been recognized through prestigious industry honors, including the Indian Icon Award presented by Dr. Kiran Bedi, the Bharat Business Award presented by Ashneer Grover, and The Excellence Award by The Hotel School. These recognitions highlight DizitalAdda's commitment to quality training, student success, and innovation in digital education.
  • At DizitalAdda, students gain real-world experience by working on live labs, recon pipelines, API and AI security assessments, and bug report writing. The focus is on building portfolios, improving practical skills, and preparing students for real security roles with confidence and industry-ready expertise.
DizitalAdda award
DizitalAdda award
DizitalAdda award

Experience Learning in a Professional Campus

Training Room
Study Zone
Corridor
Classroom
Seminar Hall
Live Session
Workshop
Group Activity
Campus Lounge

Our Greater Kailash II campus, home to the bug bounty course in Delhi, reflects a real corporate security environment — focused, distraction-free and performance-driven, with modern lab facilities. Prefer to learn from home? Join the online bug bounty course with the same live classes.

Small Batches

Max 15 students per batch for personalized attention

Corporate Setup

Real project desks & live security tools

Expert Mentors

10+ years industry experience instructors

Free Session

Book a Free Demo Class

Choose a date for your free demo session and speak with our team about the bug bounty course syllabus, AI labs, projects and career path.

SuMoTuWeThFrSa
Available
Today
Selected
Past
Select a date to book your demo session
1-hour live walkthrough of course structure and projects
100% free counselling session with zero hidden charges
Get clarity on course fit, prerequisites, and outcomes
Online and offline attendance options available
← Pick a date from the calendar

Bug Bounty Course FAQs

Short answers to common questions about the course, bug bounty careers and what you practise during training.

What is a bug bounty course?

A bug bounty course teaches you to find and responsibly report security bugs in websites, apps and APIs for rewards. Our course covers recon, OWASP Top 10, API and AI security, and report writing.

Who can join this bug bounty course?

Students, graduates, developers, IT professionals and ethical hackers. Basic computer and networking knowledge helps, and the first module covers the foundations.

Do I need coding knowledge?

No. Basic Python or Bash helps, and we teach the scripting you need for recon automation during the course.

Where is the bug bounty course in Delhi held, and is there an online option?

Classroom batches run at our Greater Kailash II campus in South Delhi. You can also join the online bug bounty course with the same live classes, labs and mentor support.

Is this an AI bug bounty course?

Yes. Every module is AI-integrated, and a dedicated Bug Bounty with Gen AI module covers AI-assisted recon, prompt injection and LLM app security testing.

Which tools will I learn?

Burp Suite, Nmap, Amass, Subfinder, httpx, ffuf, Nuclei, OWASP ZAP, Postman, Kali Linux, JWT tools and Shodan, plus AI assistants for recon and analysis.

Will I hunt on real targets?

Yes, but only on authorised bug bounty programmes, under mentor supervision and with responsible disclosure rules.

Which bug bounty platforms will I use?

HackerOne, Bugcrowd, Intigriti, YesWeHack and Synack. You learn how scope, triage and payouts work on each.

How much can I earn from bug bounty?

It depends on skill and consistency. Top hunters earn $10,000 to $100,000+ a year, and salaried security roles after the course usually start at Rs 4.8 to 8 LPA.

What if my bug is a duplicate?

You learn deeper recon and timing tactics that reduce duplicates, and how triage works on each platform.

Will I get a certificate?

Yes. You earn the DizitalAdda Expert Bug Bounty certificate after completing the course and final projects.

Do you provide placement support?

Yes, 100% Placement Assistance: CV and portfolio review, mock interviews and referrals for VAPT, pentest and security analyst roles.

Is it useful for CEH or OSCP aspirants?

Yes. It builds hands-on web pentesting skills that support CEH, OSCP and similar exams.